
Microsoft Fixes Critical eMudhra Key Vulnerability
Microsoft has urgently deployed critical Windows updates. This action follows the startling discovery of eight incredibly weak cryptographic keys. Specifically, attackers could decipher these keys in a mere 256 attempts. This severe flaw directly impacted the eMudhra Certificate Authority. Consequently, malicious actors could potentially forge authentic-looking digital certificates.
Origin of the Compromised Keys
These perilous cryptographic keys originated from eMudhra’s intermediate certificate authorities. Six of these compromised keys were actively utilized for Transport Layer Security (TLS) certificates. This fundamental protocol safeguards website connections globally. Meanwhile, the remaining two keys were explicitly designated for digital software signing. This mechanism verifies the integrity and origin of executable programs.
Surprisingly, developers generated all eight of these defective keys in April 2025. Inexplicably, their numerical values fell entirely below 256. Therefore, cracking such a minuscule cryptographic space requires virtually zero modern computational power. This fundamental error rendered the security infrastructure essentially defenseless.
Potential Threats and Exploits
Armed with such easily decipherable keys, a cybercriminal could effortlessly fabricate certificates. These forged documents would masquerade seamlessly as those issued by a trusted authority. Depending on the specific key’s designated purpose, this weakness threatened multiple systems. It compromised both the authentic verification of secure websites and the inherent trust placed in signed executable files.
Under favorable network conditions, an illicitly crafted certificate could empower an attacker significantly. They could seamlessly intercept heavily encrypted data traffic. However, Microsoft has firmly stated that its own internal corporate systems remained completely uncompromised throughout this ordeal.
Microsoft’s Defensive Strategy
The technology giant initiated its first wave of defense on October 20. The company proactively sequestered the eight affected intermediate authorities. They achieved this by adding them to the Windows untrusted certificate repository. Furthermore, engineers independently updated the Certificate Revocation List (CRLSet) for Microsoft Edge and WebView2 components.
This swift action ensured that foundational browser elements would immediately block these dangerous TLS certificates. Users did not even need to manually install a full browser update. Simultaneously, eMudhra took decisive corrective action by officially revoking the eight problematic intermediate certificates.
Escalating the Security Posture
On October 26, Microsoft escalated its defensive posture dramatically. The company decisively excised seven certificates tethered to the compromised hierarchical chains. They removed these entirely from the official trusted list. This sweeping purge included six fundamental eMudhra G3 root certificates. It also encompassed one cross-certificate belonging to AAA Certificate Services.
Eliminating trust at the root level affects a significantly broader spectrum of certificates. This approach is much more comprehensive than merely blocking the eight known vulnerable keys. Additionally, developers scheduled a parallel modification for the Edge browser on October 27. You can read the detailed Microsoft response to compromised eMudhra certificate authority keys to understand the full scope of these mitigations.
Targeted Update Packages
These extraordinary update packages are primarily vital for isolated computer terminals. Such machines do not automatically receive routine trust list synchronizations. This vulnerable category includes air-gapped networks and hardware lacking direct access to Microsoft’s certificate services. It also involves intricate systems operating with disabled Certificate Trust List (CTL) updates.
Conversely, standard internet-connected machines operate differently. These crucial modifications propagate effortlessly through routine automated mechanisms. Therefore, manual intervention is rarely necessary for the average user.
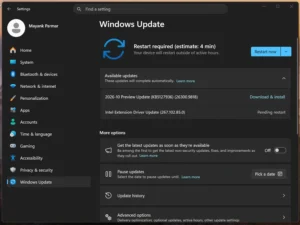
To address the diverse operating system ecosystem, Microsoft orchestrated a comprehensive patching strategy. Windows 11 versions 24H2, 25H2, and 26H2 received the KB5134133 patch. Meanwhile, version 23H2 was secured via KB5134130. The 26H1 iteration was provided with KB5134134.
Older systems were certainly not forsaken during this rollout. Windows 10 version 22H2 and the Enterprise LTSC 2021 edition obtained the KB5134125 update. Furthermore, engineers meticulously prepared bespoke standalone packages for Windows Server 2016, 2019, 2022, and 2025. System administrators can acquire these vital files directly from the official Microsoft Update Catalog.
Recommendations for Administrators
In its formal advisory communications, Microsoft strongly advises administrators to rigorously audit isolated machines. They must meticulously hunt for any certificates whose validation chains lead back to these newly excluded roots. Organizations harboring such certificates may find it absolutely imperative to request a complete reissue. Alternatively, they must establish an entirely new, fully trusted chain.
The company remains exceptionally vigilant regarding this ongoing situation. Security teams continue to scrutinize the remaining eMudhra root certificates thoroughly. Furthermore, Microsoft has openly acknowledged the distinct possibility of implementing further restrictive modifications. Finally, restoring explicit trust manually without conducting a comprehensive, professional risk assessment remains a highly hazardous endeavor.