
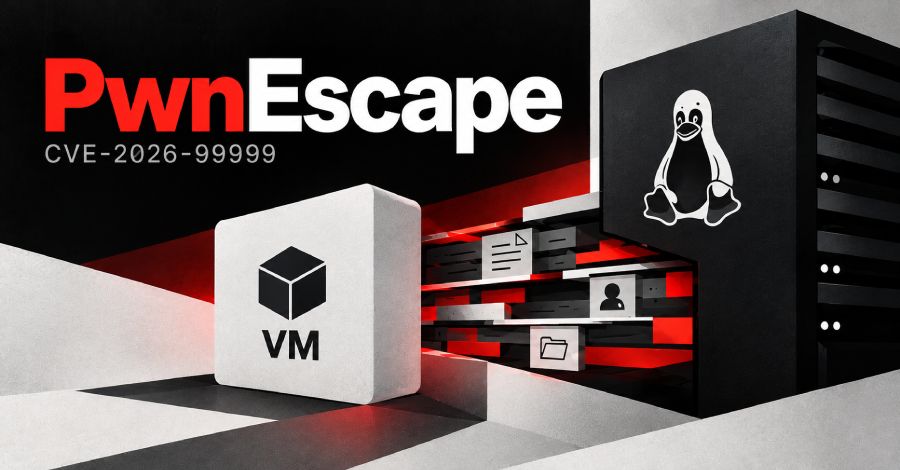
Developers have recently eliminated a critical vulnerability known as PwnEscape from the Linux kernel. This severe flaw allowed malicious actors to escape virtual machine isolation and seize total control over the underlying physical server. With an alarming CVSS score of 9.3, this bug fundamentally threatened massive cloud platforms where numerous clients share the exact same infrastructure.
The PwnEscape vulnerability officially received the identifier CVE-2026-99999. Notably, it compromises the core Linux networking stack rather than the KVM virtualization mechanism itself. Paulos Yibelo, a prominent researcher from pwn.ai, successfully demonstrated three terrifying attack scenarios. An attacker can surreptitiously read the physical server’s memory, deliberately trigger a catastrophic crash, or achieve absolute command execution with coveted root privileges. Shockingly, the attacker merely requires specially crafted network packets originating from the guest system to execute this exploit.
The Danger to Cloud Infrastructure
The most perilous scenario enables attackers to shatter the strict isolation barriers separating virtual machines from the host server. Consequently, this server actively runs applications belonging to completely different clients. By acquiring administrative rights on the host, the attacker could theoretically access the private data of other clients and maliciously interfere with the shared infrastructure. This dire threat endangers cloud services, VPS hosting providers, automated software build environments, malware analysis sandboxes, and heavily restricted execution environments designed for untrusted code.
Experts at Vercel independently confirmed the massive scale of this problem. During a routine security audit, a researcher managed to extract sensitive memory fragments from active cloud platform servers directly through operating virtual machines. One meticulously prepared packet successfully retrieved approximately 32 bytes of data, and the attacker could repeat this operation indefinitely. This sophisticated attack provided a method to gradually harvest restricted information from the host’s memory, completely bypassing the guest system’s security limitations.
Root Cause and Exploitation Details
Yibelo conclusively verified even more severe consequences within his private laboratory. Two specific network packets provided enough leverage to abruptly crash the host system. Furthermore, subsequent exploitation allowed him to execute commands with absolute root privileges. The researcher successfully replicated this attack across systems utilizing both KVM and Firecracker technologies. He even completed four successful administrative access acquisition chains following a total reboot of the test server. However, he did not demonstrate arbitrary code execution on Vercel’s live production servers.
The root cause of this vulnerability lies within the unexpected interaction of standard IPv4 processing mechanisms. The Linux kernel initially verifies the network packet header. However, during the subsequent checksum calculation process, the system might accidentally alter previously verified fields. Specially prepared control data allowed attackers to manipulate the specified IP header length, instantly expanding it from 20 to 60 bytes. During subsequent processing, the system erroneously interpreted additional memory bytes as a legitimate part of the packet and subsequently transmitted them across the network.
The Anatomy of PwnEscape
The truly unique characteristic of PwnEscape is that the initial data leak did not require breaching the hypervisor itself, which actively manages the virtual machines. Instead, the attacker targeted the core networking functions of the primary operating system, which remain accessible through the virtual network interface. According to the study’s author, this problem exposes an entire class of potential attacks where a program modifies data immediately after a security check, while other crucial components foolishly continue trusting the compromised result.
Linux developers officially acknowledged the vulnerability on October 15 and subsequently assigned it a critical severity rating of 9.3. Astoundingly, this devastating error has lurked within the code since Linux version 2.6.27. Official fixes are now included in kernel versions 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.57, 7.2.11, and 7.3-rc7. This new protection mechanism strictly prohibits the completion of the checksum calculation if the control parameters permit an overwrite of the IPv4 header. Developers are also preparing an additional packet verification step upon entry into the networking stack.
Response and Remediation
Distribution vendors have aggressively begun preparing necessary updates. On October 16, AlmaLinux successfully released patched test kernel builds for versions 8, 9, and 10. Red Hat officially confirmed the error’s impact on its products but assessed the danger slightly lower, assigning it a CVSS score of 8.8. Security experts strongly advise administrators of servers hosting virtual machines to immediately install the patched kernel versions via standard distribution updates. Fortunately, there have been no public reports regarding confirmed attacks utilizing PwnEscape in the wild.
Researchers initially discovered this vulnerability during a highly competitive contest launched by Vercel on August 18, which featured a staggering total prize pool of up to 1 million dollars. Yibelo submitted his initial report promptly on August 20, and subsequently transferred the detailed information to Linux kernel developers in September. While hunting for these elusive errors, the researcher utilized an experimental system called Omega-Pwn, which brilliantly combines automated tools and advanced language models to scrutinize source code. A human researcher ultimately performed the primary work of selecting research directions and verifying the final results.
For identifying PwnEscape, the researcher received the maximum possible reward provided by the contest, totaling an impressive $50,000. Within a mere two weeks, the organizers accepted 1,285 reports and generously paid out $242,000 to participants. However, they recognized only one discovery as genuinely critical. Vercel firmly stated that none of the submitted reports demonstrated actual access to sensitive client data. The company also engaged other major cloud market participants to help resolve the problem, as the error existed within the shared Linux code and was not dependent on any specific provider’s configuration.
Earlier in 2026, researchers had already uncovered similar methods for escaping virtual machines. The ITScape vulnerability allowed attackers to compromise a host utilizing KVM on the arm64 architecture, while Januscape specifically targeted other virtualization mechanisms. However, those previous attacks relied heavily on the specific quirks of the hypervisor or its precise configuration. PwnEscape stands out significantly because it ruthlessly exploits the common Linux networking subsystem; therefore, the potential range of vulnerable environments is vastly wider.