
Massive Data Breach Strikes Danish CPR System
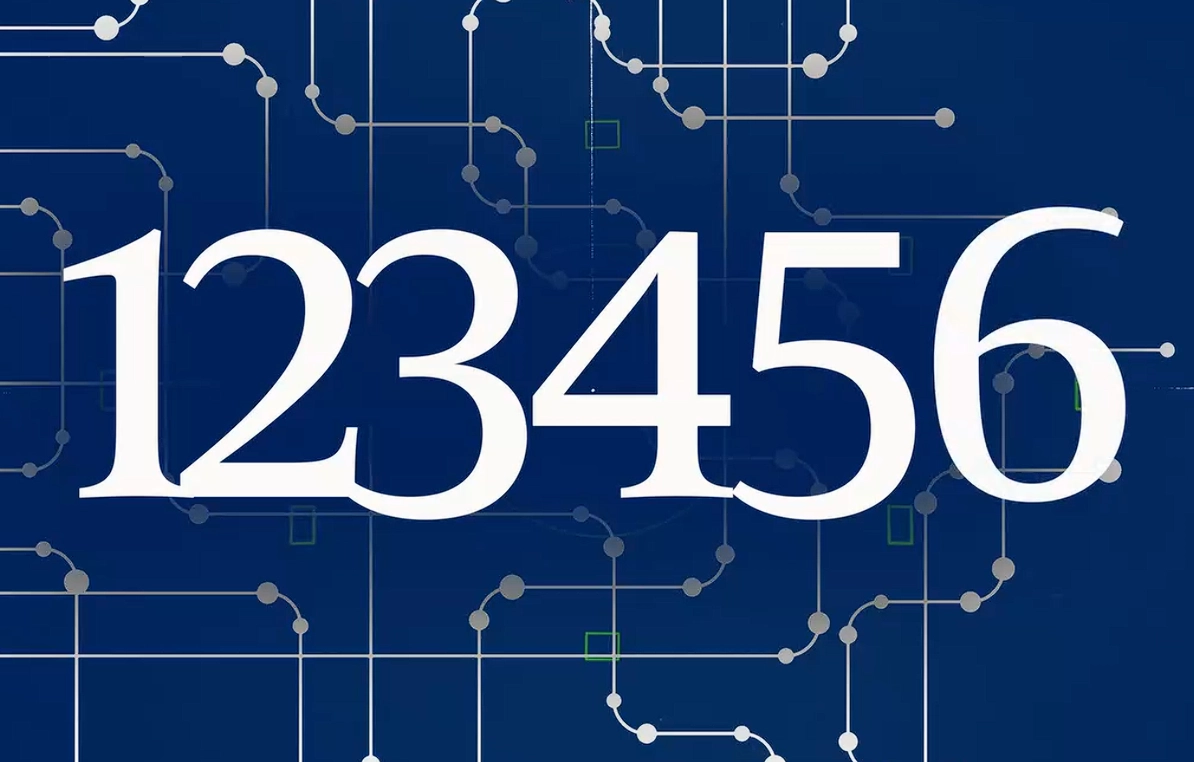
The Copenhagen Post reported a massive personal data breach affecting the Danish Civil Registration System. Disturbingly, during the cyberattack, at least three accounts associated with Pays ApS utilized the incredibly weak password “123456.” Even more concerning, one of these compromised accounts possessed full administrator privileges. A recent investigation confirmed that the 123456 password was used in a massive Danish CPR data breach.
Millions of Civil Registration Numbers Exposed
The CPR serves as Denmark’s central civil registration database. It securely stores the personal information of individuals currently residing in Denmark or those who have lived there previously. Consequently, this catastrophic security failure resulted in the unprecedented exposure of approximately 8.8 million sensitive CPR numbers.
Experts Condemn Shocking Security Failures
Jens Myrup Pedersen, a respected professor in the Department of Electrical and Computer Engineering at Aarhus University, expressed profound disbelief during a recent interview.
“This is absolutely devoid of any security; it is equivalent to leaving the front door wide open for hackers,” he stated emphatically. “If you are utilizing a standard password dictionary, ‘123456’ is undoubtedly one of the very first combinations you try. Honestly, I struggle to imagine a worse security implementation. Ultimately, this disaster was merely a matter of time.”
In response to the escalating crisis, a representative from Pays ApS issued a brief statement. “We did indeed suffer a targeted cyberattack,” the company acknowledged. “The malicious actors subsequently abused our legally acquired access rights to query sensitive information within the CPR system.”