
Let’s Encrypt Shortens Free SSL Certificate Validity
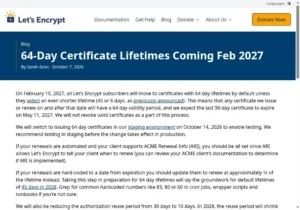
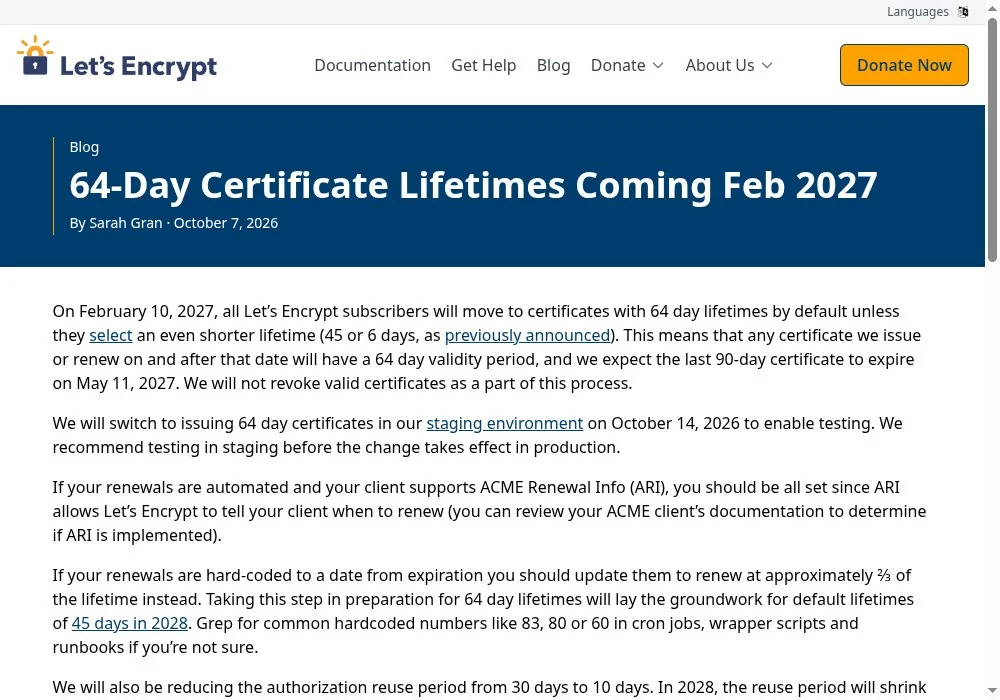
Let’s Encrypt operates as the largest website certificate authority globally. Recently, the organization released a pivotal announcement regarding digital security. Specifically, the authority will shorten the lifespan of its free SSL and TLS certificates. This major policy shift takes effect on February 10, 2027. Consequently, the standard validity period will decrease from 90 days to merely 64 days. You can review the official details concerning the 64-day certificates directly from the source.
Evolution of Certificate Lifespans
SSL and TLS certificates fundamentally secure the encrypted connections between websites and users. Historically, these essential digital credentials remained valid for one to three years. However, this lengthy standard changed when Let’s Encrypt emerged in early 2016. At that time, the institution introduced a novel 90-day validity cycle. Ultimately, this aggressive strategy successfully encouraged the widespread adoption of automated renewal mechanisms.
Future Reductions by 2028
Previously, industry reports in December 2025 highlighted the organization’s long-term vision. Let’s Encrypt explicitly plans to halve its trusted TLS certificate lifespan to 45 days by 2028. Meanwhile, the authority will initiate a public testing phase on October 14, 2026. Therefore, website administrators can voluntarily join this trial period. They can rigorously verify their issuance, deployment, and renewal workflows before the mandatory implementation date.
Mitigating Security Vulnerabilities
Shortening certificate lifespans drastically reduces the potential impact of compromised private keys. Furthermore, it limits the damage caused by erroneous certificate allocations. The upcoming 64-day validity window logically extends this protective philosophy. Additionally, Let’s Encrypt is aggressively reducing the authorization reuse period. This specific timeframe will drop from 30 days down to just 10 days. By 2028, the organization intends to compress this window further to a mere seven hours.
Actionable Steps for Administrators
Consequently, system administrators must act proactively to prevent unexpected expirations after February 2027. First, they should confirm that their ACME clients properly support ARI technology. Next, professionals must configure reliable alerts for renewal failures or impending expirations. Finally, teams must utilize the upcoming testing phase to validate their automated processes thoroughly.