
Tailscale Tailworm Vulnerability Report Exposes Critical Flaws
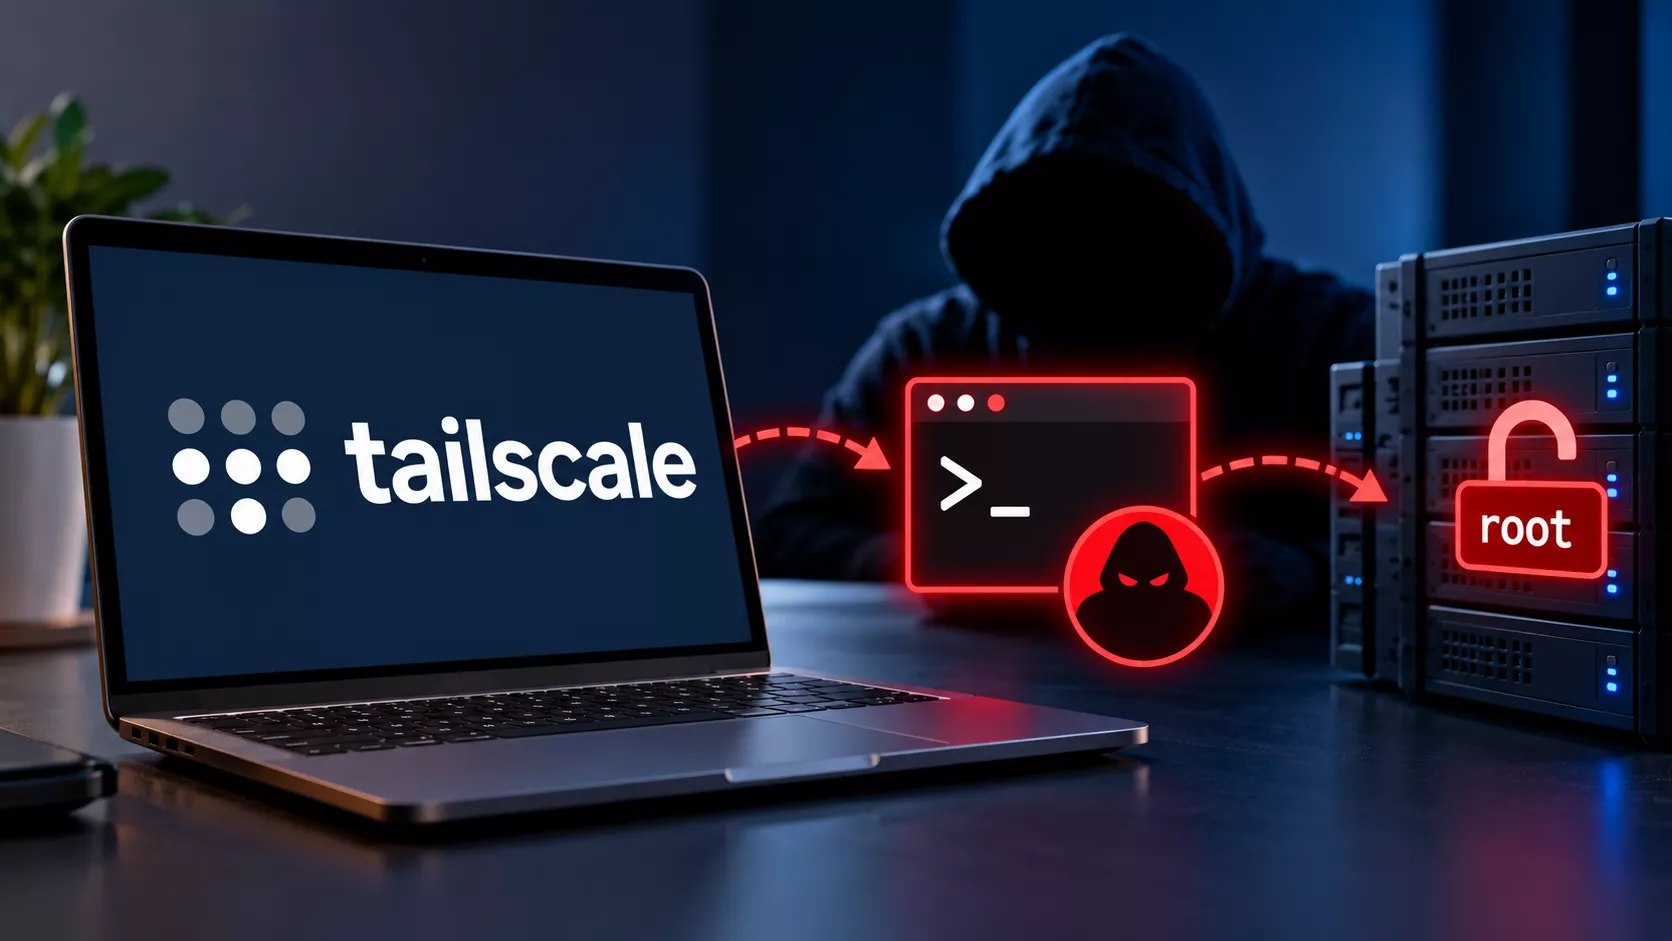
Routine server access through a supposedly secure network can rapidly devolve into absolute system control, entirely bypassing the need for administrator credentials. In a comprehensive Tailworm report, security researcher Erica Windisch of Cyberdione Labs meticulously detailed 11 security vulnerabilities afflicting Tailscale and headscale. These alarming discoveries include methods for acquiring ultimate root privileges via the integrated Tailscale SSH feature. Currently, official patches for these novel findings remain unavailable.
Analyzing the Unix Socket Forwarding Exploit
The rigorous evaluations took place between October 22 and 24, 2026, targeting Tailscale version 1.104.2 and headscale version 0.29.5. The primary vulnerability stems from Unix socket forwarding, the mechanism through which local applications communicate. Because the tailscaled service operates with root privileges, specific SSH connections prompt it to interact with secure sockets as a superuser, even if the remote participant lacks those authorized permissions.
Under laboratory conditions, an SSH session successfully accessed the Docker socket, enabling the execution of root commands, which included reading highly classified files. Another sophisticated technique exploited a race condition between socket path verification and the subsequent operation. Windisch also demonstrated the feasibility of replacing secure sockets and intercepting device registration keys. However, establishing a persistent foothold within the network using these stolen keys was only achievable when Tailnet Lock was explicitly disabled.
Propagation and Additional Discoveries
Executing this attack requires malicious control over a device explicitly permitted by network protocols to connect to the target server via Tailscale SSH with forwarding enabled. Merely installing Tailscale on a machine is fundamentally insufficient. In a controlled laboratory setting, an automated attack cascaded to other authorized nodes in less than a second per transition. Fortunately, there is currently no evidence of such rampant propagation occurring within real-world networks.
Additional discoveries impact experimental application connectors, Tailscale Serve, DERP relays, and the headscale server. The conn25 function inadvertently allowed traffic misdirection toward addresses outside the approved boundaries, encompassing internal services and cloud-based credential issuance interfaces. Furthermore, vulnerabilities within headscale allow unauthenticated actors to overwhelm the memory, effectively paralyzing the connection of new devices.
Corporate Response and Mitigation Strategies
Tailscale has received the comprehensive dossier, and Vice President of Engineering Mike Shaver verified that the corporation was already investigating analogous issues and is actively formulating fixes. The development team has yet to formally validate every single claim and is currently delineating the affected configurations. According to recent Tailscale vulnerability reports on Reddit, these novel issues currently lack assigned CVE identifiers or official CVSS 3.1 or 4.0 severity scores. Nonetheless, the report author categorized the most perilous flaws as carrying a critically high level of risk.
Recommended Security Measures
Pending the release of official patches, Tailscale advises administrators to stringently limit SSH access and disable unnecessary forwarding by setting the parameter TS_SSH_DISABLE_FORWARDING=1, followed by restarting the tailscaled daemon. The company does not yet recommend completely disabling Tailscale SSH. Within headscale 0.29.5, existing access protocols do not allow for the isolated prohibition of forwarding; therefore, authorized connections mandate heightened vigilance.
Earlier this July, the ecosystem successfully resolved a separate access rights dilemma. OpenWrt developers patched the luci-app-tailscale-community vulnerability, which previously permitted the execution of root commands directly from the control panel. However, Tailworm involves entirely distinct codebases and attack vectors. For the time being, these profound conclusions rely solely upon the report author’s private trials, as an independent public verification of all 11 discoveries remains pending.