
Microsoft Warns of Impending Update Service Disconnections
Microsoft has issued a critical warning that certain outdated or unsupported Windows devices may lose access to Windows Update services in 2027.
The technology giant announced that a specific set of certificates, which verify trusted connections between devices and Windows Update servers, will officially expire on May 17 and June 19, 2027. Consequently, affected devices must proactively install updates containing the new certificates or upgrade to a fully supported Windows version.
Understanding the Certificate Rotation
As detailed in a recent update on the Windows IT Pro blog, Windows Update relies on a certificate-based trust mechanism to ensure devices connect securely to authenticated servers. Because these digital certificates possess strict validity periods, administrators must replace them before expiration. Fortunately, Microsoft has seamlessly delivered new certificates to the majority of devices through standard monthly updates. However, some older or unpatched systems still require immediate administrator intervention to navigate this Windows Update certificate expiration safely.
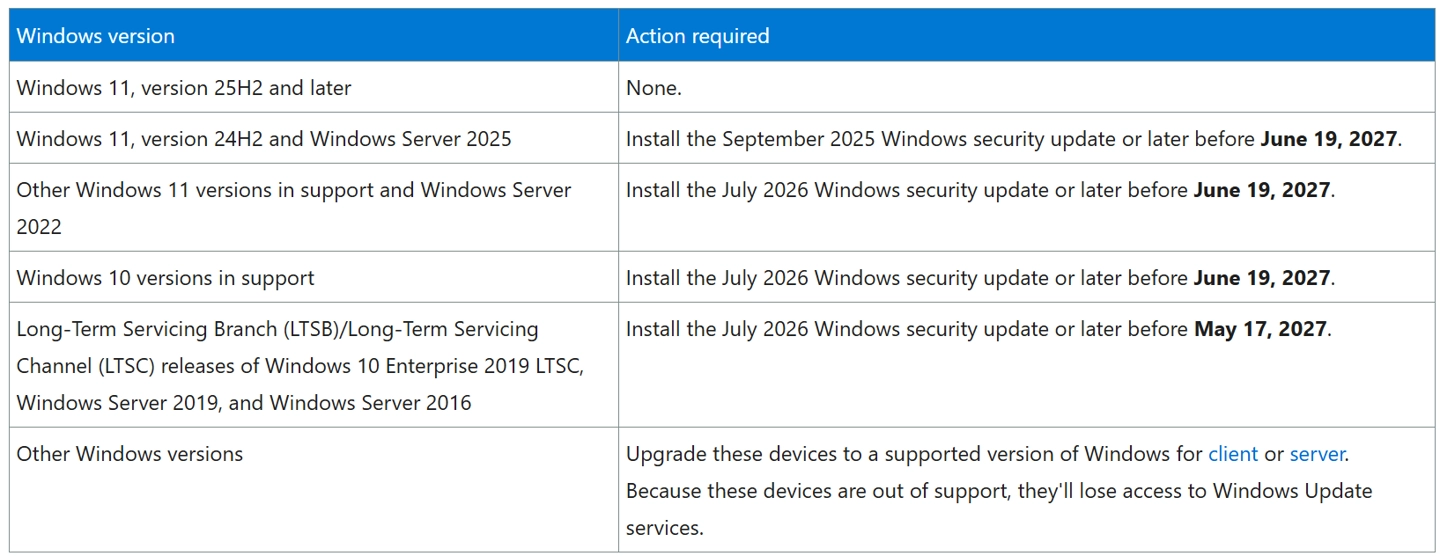
According to the published guidelines, devices running Windows 11 version 25H2 and subsequent iterations require no additional action. Conversely, devices operating on Windows 11 version 24H2 and Windows Server 2025 must install Windows security updates released in or after September 2025 before the June 19, 2027 deadline. Other supported Windows 11 editions, Windows Server 2022, and supported Windows 10 versions must implement security updates released in or after July 2026 before that same critical cutoff date.
Specific Deadlines for Enterprise Systems
For environments utilizing Windows 10 Enterprise 2019 LTSC, Windows Server 2019, and Windows Server 2016, Microsoft mandates the installation of security updates released in or after July 2026 prior to May 17, 2027. Furthermore, systems running Windows versions that have already reached their end-of-support lifecycle should be urgently upgraded to a supported client or server edition.
Microsoft clarified that devices running supported versions with the prerequisite updates installed will seamlessly continue receiving updates during this certificate rotation. If supported devices remain unpatched, they will lose access to the Windows Update service immediately after their respective certificates expire. For machines still languishing on unsupported operating systems, Microsoft stated unequivocally that these devices will permanently forfeit their access to the update infrastructure.
Deployment Recommendations for Administrators
For systems demanding manual remediation, administrators can download and execute the necessary updates directly through the Microsoft Update Catalog. Alternatively, they may deploy these vital patches uniformly using established device management tools. Microsoft explicitly emphasized that devices retrieving updates via Windows Server Update Services (WSUS) remain completely unaffected by this architectural transition.
Ultimately, Microsoft strongly advises enterprise IT administrators to proactively audit their infrastructure for devices running antiquated or unsupported Windows systems. Administrators should guarantee that supported devices promptly receive their monthly updates. Formulating a comprehensive upgrade strategy before the impending deadlines in May and June 2027 will significantly mitigate the risk of update disruptions and severe security vulnerabilities.