
P7 DarkSword Spyware Targets Apple iPhones
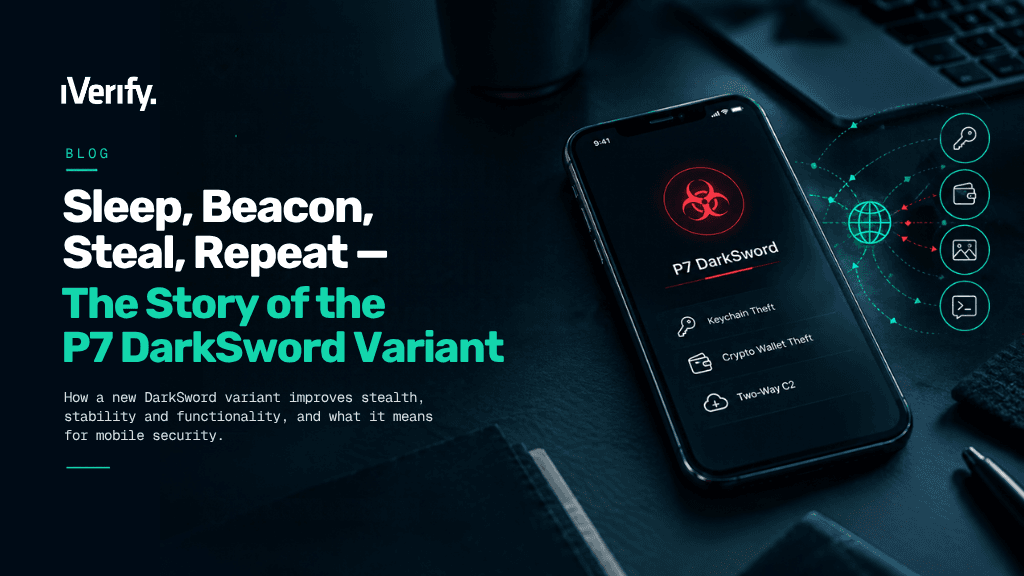
On October 8, the cybersecurity firm iVerify published a report exposing an iOS spyware variant. This sophisticated malware is dubbed P7 DarkSword. It specifically targets Apple iPhone devices. Furthermore, the malicious software masterfully minimizes its digital footprint. Meanwhile, it maintains remote control communications every 15 seconds. Through this persistent connection, the spyware systematically exfiltrates photographs, personal notes, and arbitrary files. You can read the complete DarkSword variant threat research for a deeper technical analysis.
The Discovery of a New Threat
This profound discovery originated from a meticulous investigation in August. Researchers were examining a previous DarkSword infection. Through rigorous analysis, security experts confirmed a previously undocumented iteration. They designated this new threat as P7 DarkSword. This moniker originates from the “p7_” variable prefix embedded within the modified source code. Ultimately, this devastating upgrade significantly enhances the stealth and stability of the malware.
Advanced Evasion Techniques
The sophisticated program eradicates HTTP requests and purges debugging logs from the system logger. Moreover, it deliberately reduces the frequency of process injections. The spyware cleverly exploits browser local storage to prevent redundant device exploitation. The insidious implant actively injects itself into the native SpringBoard process of the iPhone. Subsequently, it transmits a beacon to the command server every 15 seconds.
Remote Command Capabilities
From a remote location, adversaries can dynamically adjust this communication interval. They can seamlessly issue commands to read files or upload photographs. Additionally, the attackers can enumerate installed applications, scan the internal disk, and execute JavaScript code. P7 DarkSword possesses the capability to convert highly sensitive keychain data into JSON format. Afterward, it rapidly exfiltrates this valuable information.
Targeting Cryptocurrency Wallets
The malware relentlessly scans the device for installed cryptocurrency wallet applications. In fact, the analyzed research sample demonstrates a dedicated extraction command. This command successfully harvests sensitive data from the imToken wallet. Moreover, this relentless variant can upload private photograph galleries and Apple Notes databases. It also targets restricted application sandbox files and specific directories.
Continuous Evolution of Spyware
The spyware utilizes specific network endpoints for distinct data streams. One endpoint strictly handles keychain and cryptocurrency wallet data. Another endpoint processes image uploads, and a third manages personal notes. According to iVerify, the emergence of P7 DarkSword demonstrates continuous iteration by the operators. In stark contrast to automated variants, the architect invested substantial effort into manual code modification. Ultimately, they succeeded in shrinking the forensic footprint while expanding their espionage capabilities.